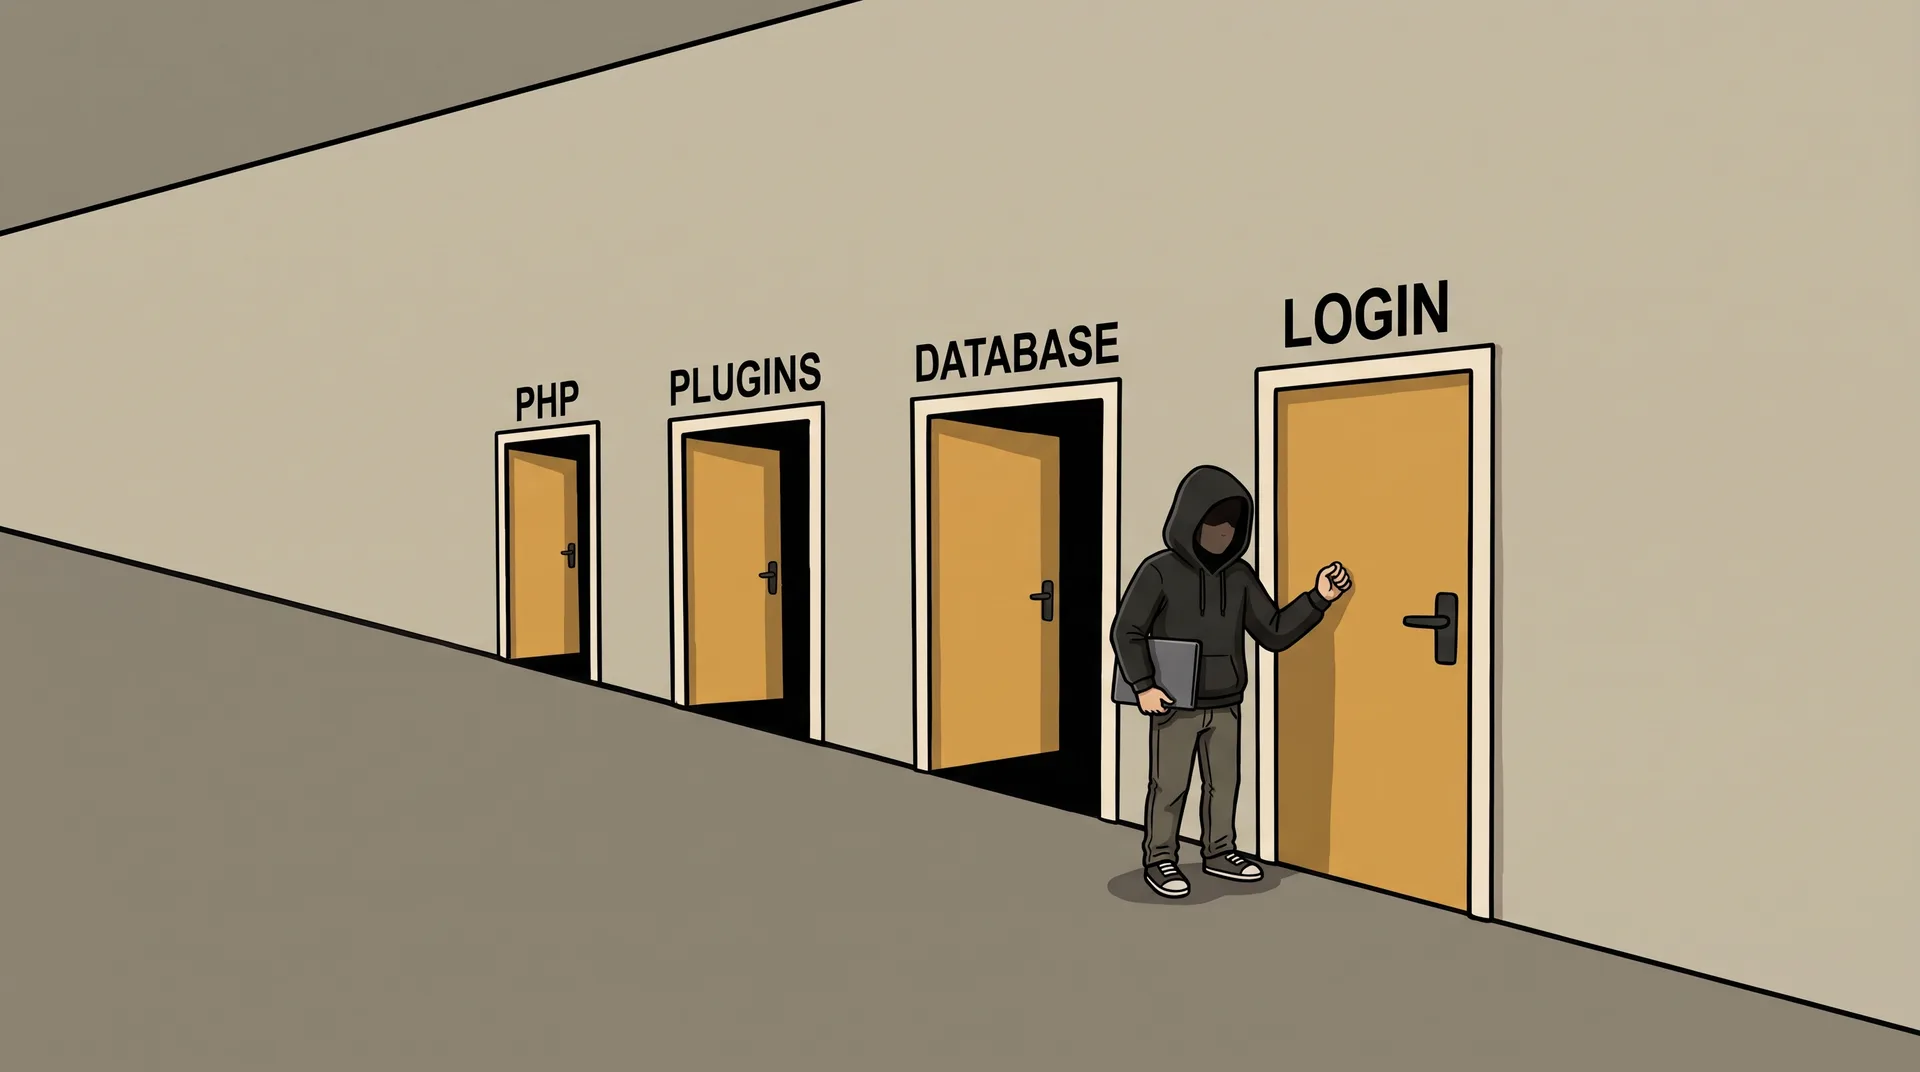
October was a rough month for website security. In the space of four days, a backup service used by hundreds of thousands of WordPress sites was breached, and a critical flaw was found in PHP, the software that WordPress and most of the web runs on.
If you're a Graphic Detail client, you were covered. Every one of our client servers was patched by 1:20pm on 22 October, about ten hours after the fix was released.
This article explains what happened, what we did, and why we're building our next generation of websites on a platform where this whole category of problem doesn't exist.
What happened
"PHP2Shell": a critical flaw in PHP itself
On 21 October, US time, the PHP project released emergency fixes for two vulnerabilities, each rated 9.2 out of 10 for severity. Together they could let an attacker take control of a web server without logging in, and read passwords and other sensitive data straight out of its memory.
Researchers say every version of PHP back to 2012 was affected, and they showed the attack working against the latest version of WordPress. Details leaked a day early, so attacks began before the fix was even available. Cloudflare reported hundreds of thousands of attempts within two hours of the announcement, and millions by the next day. (Patchstack, Codeable)
It was serious enough that the Dutch government took its national login service and parliament website offline as a precaution while it waited for the fix. (Search Engine Journal)
Because the flaw was in PHP rather than WordPress, there was nothing to update in the WordPress dashboard. The fix had to be applied on the server itself, by whoever looks after it.
Stolen keys from a WordPress backup service
A few days earlier, the company behind UpdraftPlus, a popular WordPress backup plugin, discovered its customer systems had been breached. Attackers used stolen connection keys to quietly install backdoors on client websites, potentially exposing around 400,000 sites. Even fully updated sites were affected, because the attackers didn't need to break in: they had the keys. (BleepingComputer)
What we did for your site
The PHP fix reached New Zealand at around 3am on 22 October. Our server engineer, Thomas, had updated PHP on every one of our client servers by 1:20pm that day.
None of our client sites use UpdraftPlus, so the backup key breach didn't touch them.
You didn't need to log in, check a version number or call anyone. That's the point of having us look after your site.
Why websites like this need constant care
WordPress has served our clients well for many years, and it still does. It powers around four in ten websites worldwide, and that popularity is also what makes it the internet's biggest target. (W3Techs)
A WordPress site builds each page on the fly, every time someone visits, using software running on a live server. That means several layers need to be kept up to date, all the time:
- The server and PHP, where October's flaw sat.
- WordPress itself, which releases regular updates.
- Plugins and themes, each from a different developer with its own update cycle.
- Third-party services like backup tools that hold keys to your site.
None of that is a problem when someone is watching every layer, every week. That's what we do, and it's why October passed without incident for our clients. But it does mean the job never ends.
Where we're heading
For new builds and rebuilds, we've moved to a platform where this whole class of risk doesn't exist.
Our Foundation websites are built differently. Every page is created ahead of time as a finished page, then delivered from the same cloud infrastructure trusted by some of the world's biggest brands. When someone visits, there's no PHP, no WordPress database and no plugins running behind the scenes, just a finished page, delivered almost instantly.
Here's how the two compare:
| WordPress site | Foundation website | |
|---|---|---|
| PHP on the server | Yes, kept patched by us | None |
| Plugins | Several, each needing updates | None |
| WordPress database behind the site | Yes | None |
| WordPress login page on your domain | Yes | None |
| Affected by October's incidents | Needed same-day patching | No |
| Speed on a phone | Good, with tuning | Loads almost instantly |
No website is ever completely risk-free, and we won't pretend otherwise. But with no PHP, plugins or WordPress database to attack, the most common ways into a website simply aren't there. When the next big PHP or WordPress vulnerability makes the news, Foundation sites shouldn't need an emergency fix.
What Foundation means for you
One monthly subscription covers the design, build and ongoing care of a website built to win work, from the first design through to the results.
- Built to generate leads. A fast, modern website designed around one goal: turning visitors into calls and enquiries.
- Serious technology, no headaches. Your site runs on the same cloud infrastructure trusted by some of the world's biggest brands. It loads almost instantly on a phone, doesn't go down under pressure, and has no plugins for hackers to target.
- Your Google reviews, live on your site. Updated automatically, so every visitor sees why customers recommend you.
- Found by Google and by AI. Every page is set up with the technical foundations search engines and AI tools need to understand exactly what you do and where you work.
- Unlimited changes. New photos, prices, services or whole pages, whenever you need them.
- A plain-English report every month, showing how many people found you and got in touch.
- A quarterly catch-up with us, to review results, plan what's next and keep the momentum building.
When you're ready to do more, ongoing blog content, Google Business Profile management and ongoing SEO are available as add-ons.
Moving to Foundation
If your site is on WordPress with us, we're keeping it protected and patched, and you don't need to change anything.
But if you'd like a website that works harder to bring in new business, and doesn't need emergency fixes for flaws like October's, Foundation is built for exactly that. It's $299 + GST per month, with design and build included and no setup fee. There's a 12-month minimum, then it's month to month with 30 days' notice, and the website is yours to keep, whatever happens.
We handle the whole move, including page-by-page redirects to protect your search rankings, and switch over with no downtime.
Sources
- Major security alert: PHP vulnerable to critical RCE, attacks ongoing, Patchstack
- Critical PHP core vulnerabilities affect websites, including WordPress, Search Engine Journal
- PHP security release on 21 October 2026: what WordPress site owners need to do, Codeable
- Stolen UpdraftCentral keys used to backdoor WordPress sites, BleepingComputer
- Usage statistics of WordPress, W3Techs
Graphic Detail is an Auckland web design studio that looks after your whole online presence.
Ready to talk about your site?
Email Ross at ross@graphicdetail.co.nz or call 09 418 3127.
See how it worksCommon questions
Was my WordPress site affected by the October PHP flaw?
If your site is hosted with Graphic Detail, every client server was patched by 1:20pm on 22 October, about ten hours after the fix was released, and you didn't need to do anything. If your site is with another provider, check with them that PHP has been updated.
Do I need to update anything in WordPress?
No. The flaw was in PHP rather than WordPress, so there was nothing to update in the WordPress dashboard. The fix had to be applied on the server itself, by whoever looks after it.
Is a Foundation website completely secure?
No website is ever completely risk-free. But with no PHP, plugins or WordPress database to attack, the most common ways into a website aren't there, so the next big PHP or WordPress vulnerability shouldn't need an emergency fix.
Do I have to move off WordPress?
No. If your site is on WordPress with us, we're keeping it protected and patched. Foundation is there if you want a website that works harder to bring in new business and doesn't need emergency fixes for flaws like October's.
What does it cost to move to Foundation?
Foundation is $299 + GST per month, with design and build included and no setup fee. There's a 12-month minimum, then it's month to month with 30 days' notice, and the website is yours to keep. We handle the whole move, including page-by-page redirects, with no downtime.